
A US-based technology company engaged InnReg to strengthen compliance for its AI-powered employee benefits platform. The platform helps employees choose, use, and manage workplace health and financial benefits.
The company works with employers, insurance carriers, brokers, and benefits technology providers. Operating at a national scale, it supports millions of employees through benefits selection, claims support, and financial wellness tools.
As the company expanded its products and AI capabilities, it needed to manage a growing range of requirements involving health information, privacy, cybersecurity, insurance, AI governance, and financial services.

Objective
The client engaged InnReg to strengthen its regulatory compliance framework as its product offering and use of sensitive data continued to expand.
The engagement was designed to help the client:
Evaluate regulatory requirements across its products and data flows
Strengthen its HIPAA, cybersecurity, and data-governance framework
Support recurring NYDFS assessments and filings
Translate existing policies into more practical compliance processes
Assess regulatory considerations associated with new products, partnerships, and potential transactions
InnReg’s role was to supplement the client’s existing legal, security, and governance functions with regulatory analysis, structured compliance tools, and cross-functional support.

See also:
Challenges
The client’s business model did not fit neatly within a single regulatory framework. Its main challenges included:
Map existing controls to overlapping regulations. The client needed to align its established security and compliance controls with HIPAA, NYDFS, state insurance laws, and other applicable requirements.
Trace sensitive data across complex workflows. Health and benefits information moved among employers, administrators, carriers, data providers, and the client’s systems. This required clarity around access, permitted uses, contracts, retention, and incident response.
Establish governance for expanding AI capabilities. The client needed a practical framework for addressing privacy, data use, internal accountability, and emerging regulatory expectations.
Assess the impact of product expansion. Claims automation, financial wellness services, partnerships, and potential transactions could introduce new privacy, insurance, or financial-services requirements.
Turn policies into operational evidence. Existing policies needed to be connected to specific controls, supporting documentation, responsible owners, and recurring reviews.
Coordinate compliance across multiple teams. Annual filings and regulatory reviews required timely input from legal, security, product, finance, operations, and other internal stakeholders.
InnReg's Solution
InnReg provided regulatory analysis and practical compliance support tailored to the client’s products, data environment, and internal structure. The engagement included:
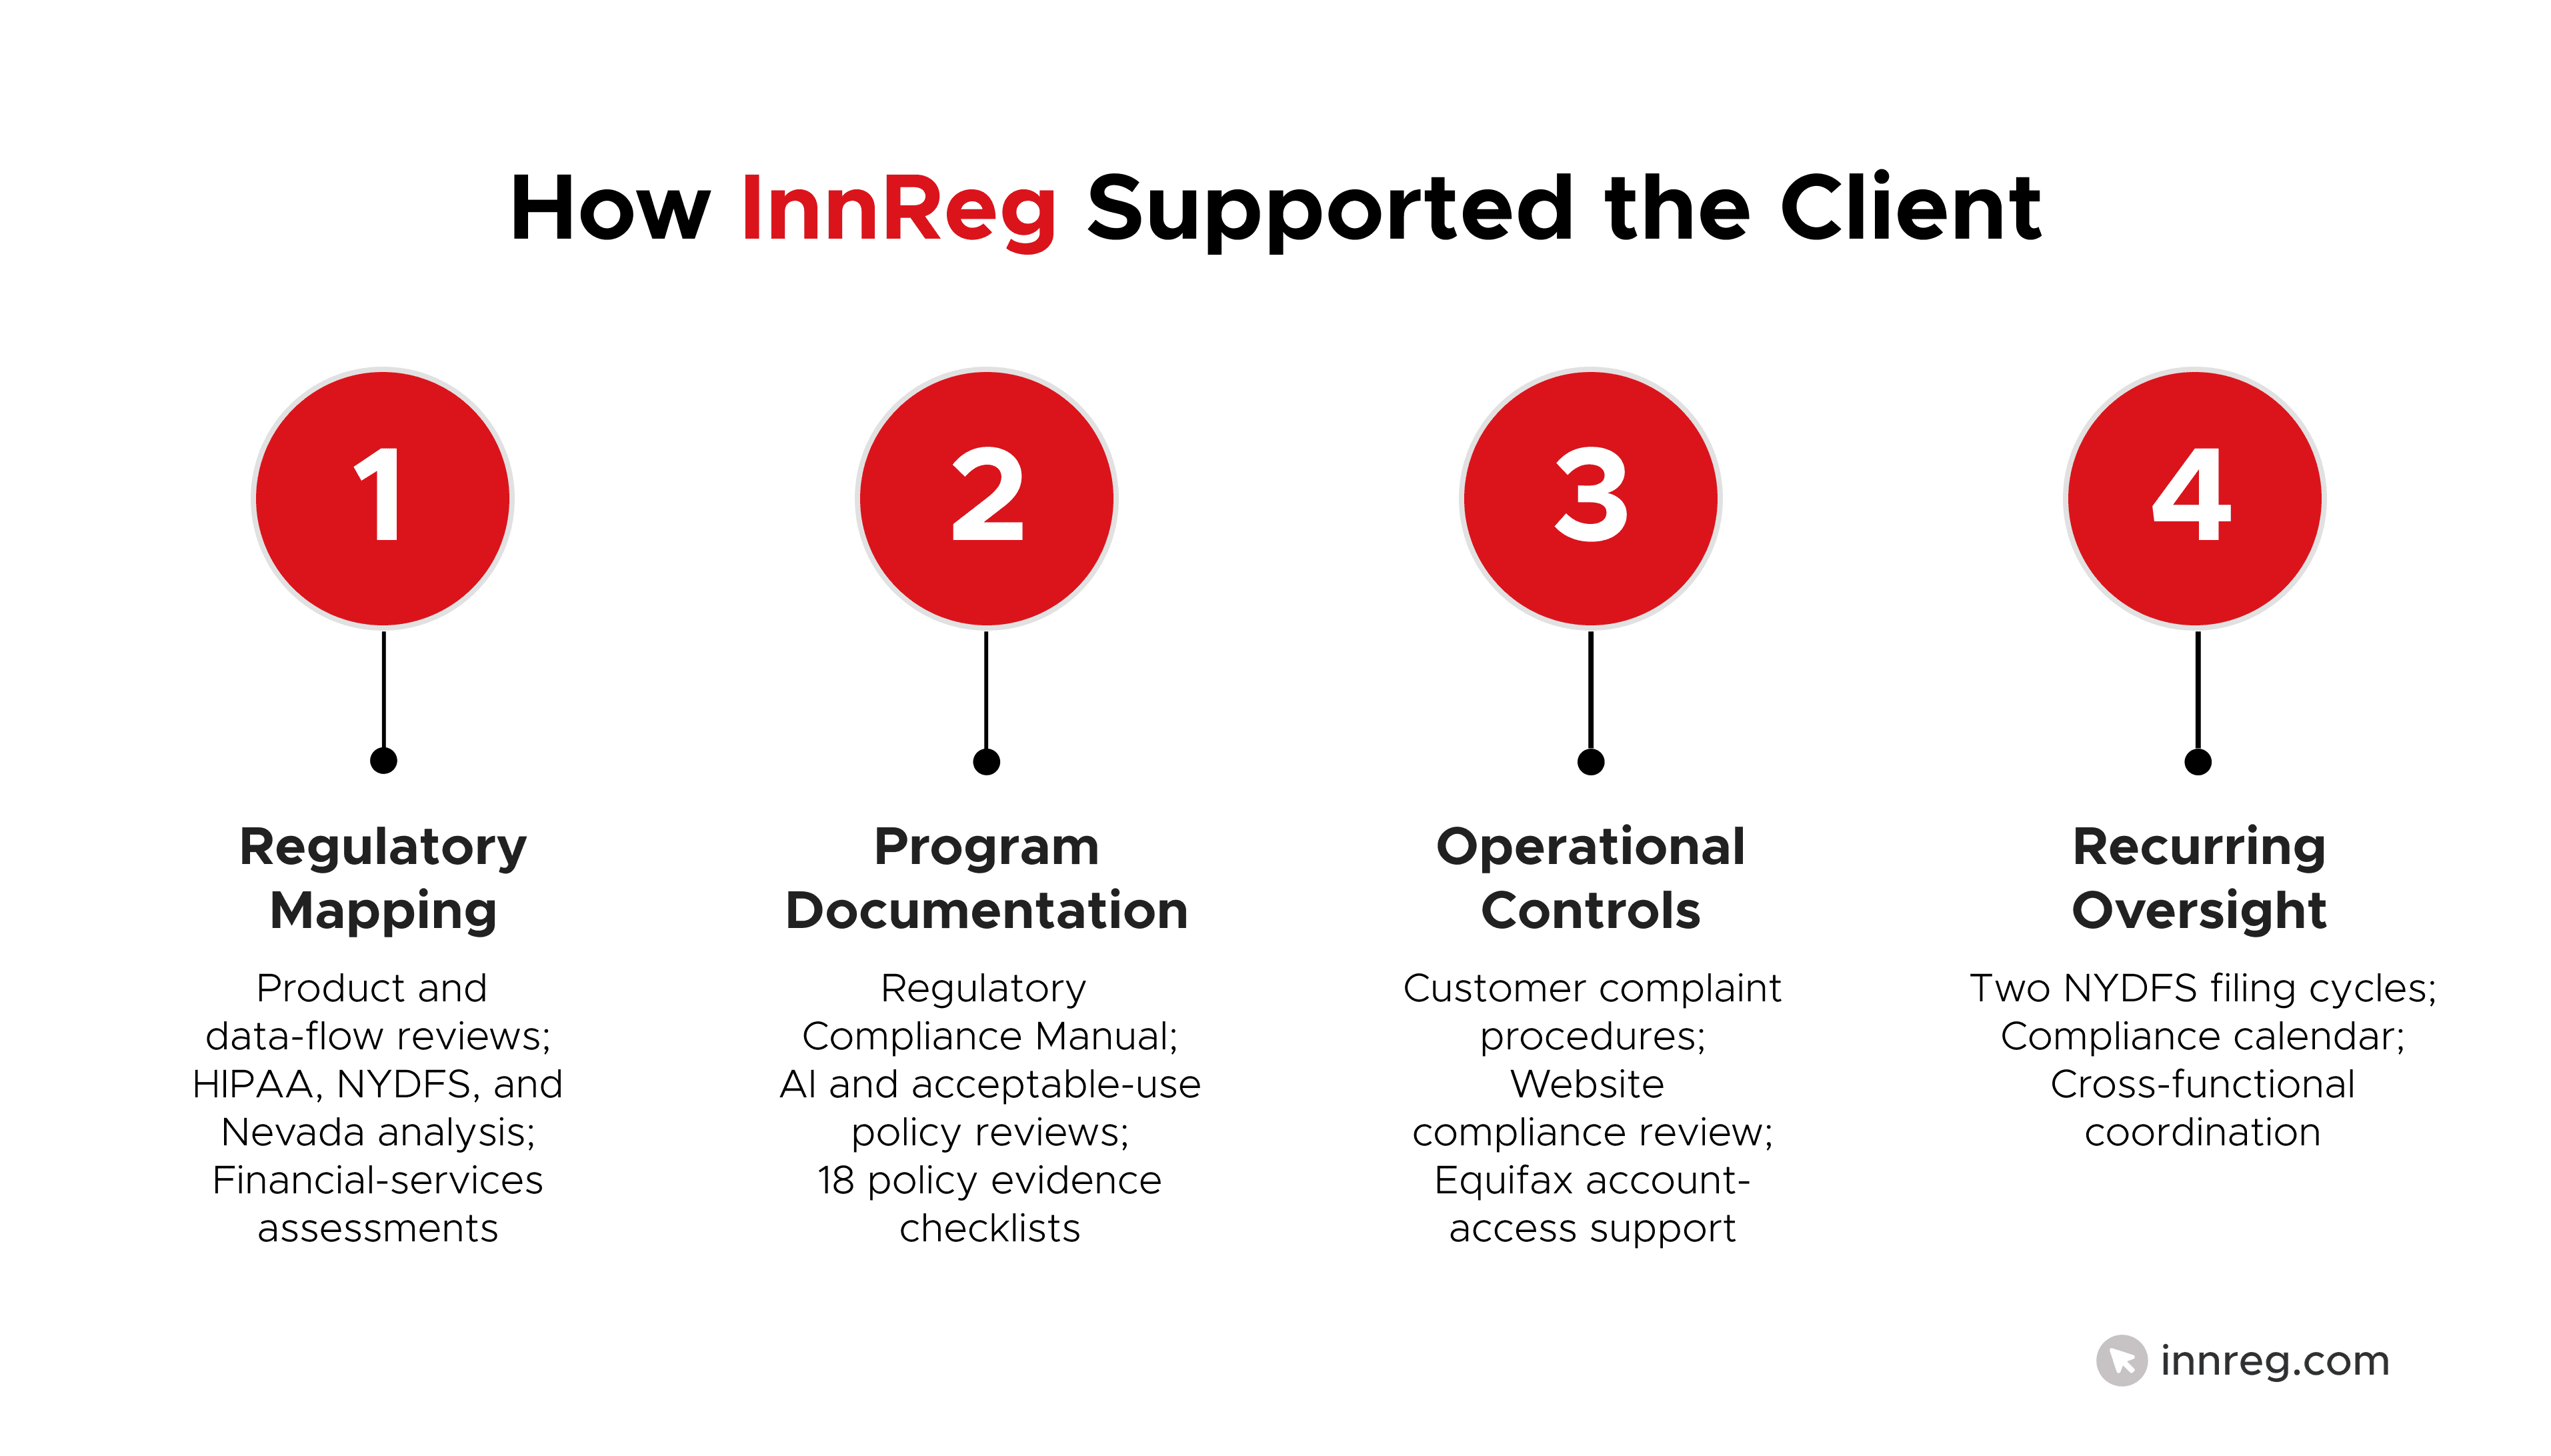
Reviewing products and data flows. InnReg examined how sensitive information moved among employers, administrators, carriers, data providers, and the client’s systems.
Mapping privacy, cybersecurity, and AI requirements. InnReg developed a compliance checklist and reviewed the client’s cybersecurity program against HIPAA, NYDFS, and applicable state requirements. The team also created a framework for applying privacy and governance principles to AI-enabled healthcare technology.
Supporting annual NYDFS compliance. InnReg prepared checklists, reviewed supporting evidence, coordinated stakeholder input, and tracked outstanding items across multiple annual filing cycles.
Strengthening policies and implementation documentation. InnReg developed a Regulatory Compliance Manual, reviewed the client’s AI and acceptable-use policies, and created checklists connecting internal policies to controls, evidence, owners, and recurring reviews.
Addressing specific operational compliance needs. InnReg reviewed website communications, recommended improvements to its customer complaint process, and supported permissible-purpose and recredentialing requirements related to a third-party data provider. The client implemented the complaint-process recommendations.
Organizing ongoing compliance activities. InnReg created a compliance calendar covering privacy, cybersecurity, AI governance, policy reviews, business continuity, third-party risk, and other recurring obligations.
Evaluating expansion-related regulatory questions. InnReg assessed whether new products and financial wellness activities could introduce additional licensing or compliance requirements. The team also provided regulatory and compliance support for a potential acquisition, separate from the transaction’s financial, technical, and operational review.

Client Results
The engagement gave the client a clearer operating structure for managing privacy, cybersecurity, AI governance, insurance, and financial wellness compliance. Internal teams gained better visibility into how regulatory requirements connected to specific products, data relationships, and business functions.
The client completed multiple annual NYDFS compliance cycles with InnReg’s support, including a submission completed ahead of the applicable deadline.
The client also implemented InnReg’s recommendations for its customer complaint process. Product and regulatory reviews provided a more consistent basis for evaluating new features, partnerships, and financial wellness activities.
InnReg’s work supplemented the client’s existing legal, security, and governance functions. This helped the teams work from a shared regulatory framework and provided a practical foundation for managing recurring compliance work as the platform continued to develop.
How Can InnReg Help?
InnReg can help complex RIA models with coordinate compliance across teams, handle sensitive customer information across vendors and workflows while strengthening policies and implementation documentation. If you need compliance support without the cost of a full-time hire, reach out to speak to an expert today.


